 Greek
 English
Amaliada
67 Eptanisou & Karaiskaki

Complete the form and our team will guide you to the right training or certification programme.
Acquire specialised expertise in determining, implementing and managing information security controls
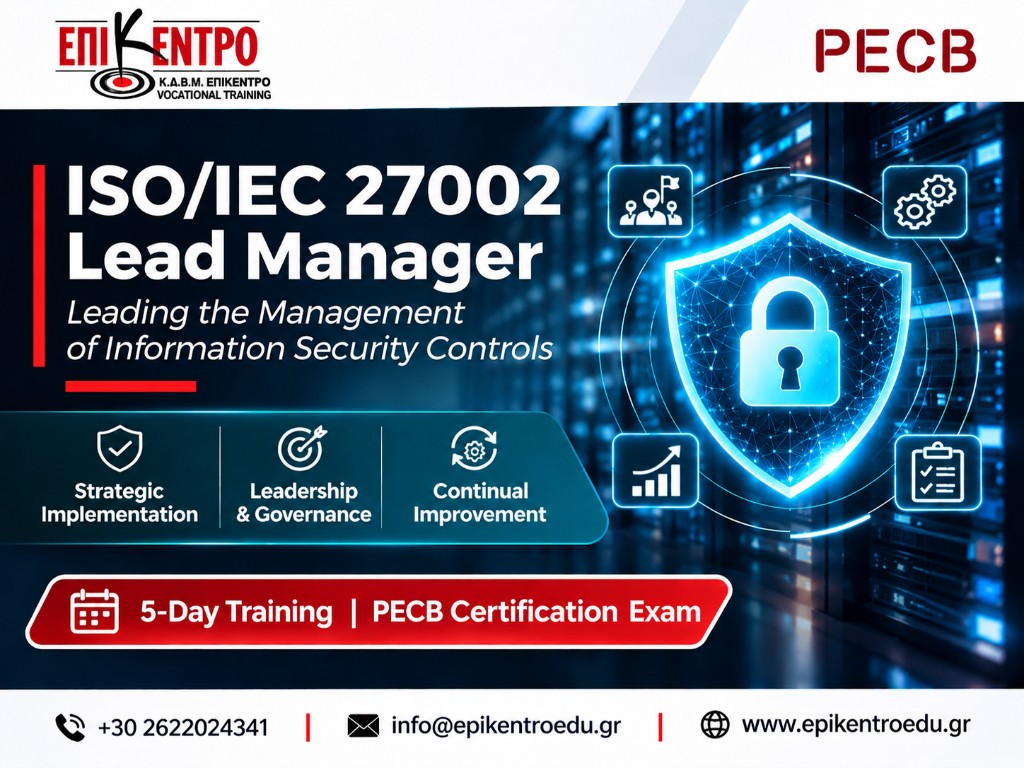
The KDBM EPIKENTRO VOCATIONAL TRAINING, a KDBM certified by the National Organisation for the Certification of Qualifications and Vocational Guidance (EOPPEP) and the Ministry of Education, Religious Affairs and Sports (certification code: 2000540), in cooperation with PECB (see the cooperation agreement here), delivers the training programme ISO/IEC 27002 Lead Manager.
The training programme is designed to develop the necessary knowledge and skills required to support an organisation in effectively identifying, implementing and managing information security controls.
Through the training, participants gain the ability to interpret and adapt the controls of ISO/IEC 27002 to the particular needs, activities and operating environment of each organisation. They also become familiar with methods for selecting appropriate controls, taking into account the risks identified through the risk assessment process.
The PECB Certified ISO/IEC 27002 Lead Manager certification confirms that its holder has the necessary expertise to identify and manage appropriate information security controls, with the aim of effectively addressing an organisation's risks.
Upon completion of the programme, certification exams follow. Successful candidates can apply for the “PECB Certified ISO/IEC 27002 Lead Manager” certificate.
The training programme is aimed at:
Upon successful completion of the programme, participants will be able to:
The training process combines theoretical training with practical application, through detailed guidance, examples and exercises related to implementing and managing information security controls.
Specifically, it includes:
Participation in the programme requires a basic understanding of the ISO/IEC 27002 standard and comprehensive knowledge of information security controls.
contact tel.: 2622024341
email: info@epikentroedu.gr
Reach us at any of our branch offices.
67 Eptanisou & Karaiskaki
Heroes’ Square (Plateia Iroon)
1 Dounia St




We respect your privacy
We use cookies to offer you the best possible experience on our website. You can learn more about the cookies we use or disable them in settings. Cookie policy.
We use cookies for the operation of the site and, with your consent, for statistics. Privacy Policy
Necessary cookies are absolutely essential for the proper functioning of the website. This category includes only cookies that ensure basic functionalities and security features of the website. These cookies do not store any personal information.
Used for anonymous traffic statistics via Google Analytics. Your consent is required.