 Greek
 English
Amaliada
67 Eptanisou & Karaiskaki

Complete the form and our team will guide you to the right training or certification programme.
Develop specialised skills in managing the security and privacy protection of IoT systems
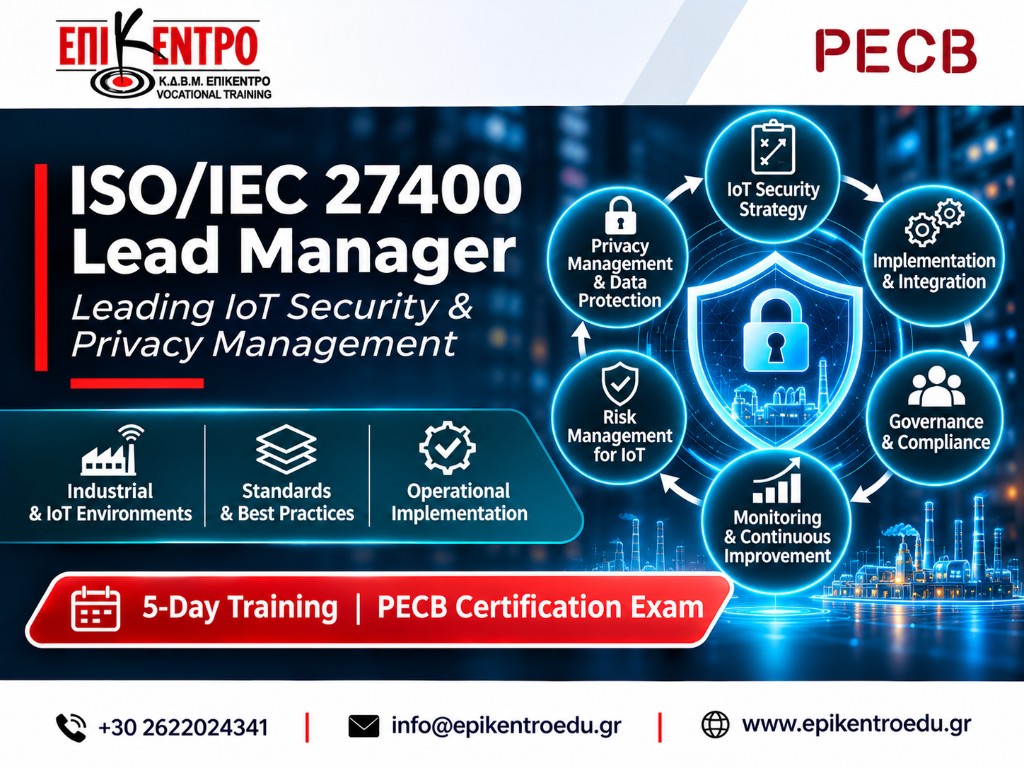
The KDBM EPIKENTRO VOCATIONAL TRAINING, a KDBM certified by the National Organisation for the Certification of Qualifications and Vocational Guidance (EOPPEP) and the Ministry of Education, Religious Affairs and Sports (certification code: 2000540), in cooperation with PECB (see the cooperation agreement here), delivers the training programme ISO/IEC 27400 Lead Manager.
The training programme offers specialised knowledge of the principles, strategies and best practices of cybersecurity in the Internet of Things (IoT) environment. It focuses on the key security and privacy risks in IoT systems, as well as on the corresponding controls set out in the international standard ISO/IEC 27400.
Through the training, participants gain the expertise needed to design, develop, implement, manage and continually improve IoT security measures in an organisation.
The ISO/IEC 27400 Lead Manager training programme is aimed at professionals who are responsible for managing IoT-related risks. It covers important topics such as the IoT system lifecycle, asset management, security incident response and the continual improvement of related processes.
Through practical exercises and discussions based on real professional scenarios, participants develop the skills required to strengthen organisational security and protect sensitive data in IoT environments. On completing the programme, they will be well prepared to take on a leading role in safeguarding connected systems and strengthening the long-term resilience of organisations.
The training programme is aimed at:
Upon successful completion of the programme, participants will be able to:
The training process combines theoretical instruction with hands-on practice, with an emphasis on modern methodologies and best practices for managing security and privacy in IoT systems.
The programme includes written-answer exercises, multiple-choice questions, practical examples and the application of best practices in security and privacy management.
PECB offers different formats for delivering its training programmes, from traditional classroom training to modern, technology-supported training solutions.
Participants should be familiar with the ISO/IEC 27400 standard and related international standards, such as ISO/IEC 30141, ISO/IEC/IEEE 12207, ISO/IEC 27001 and ISO/IEC 27005, as well as have a basic knowledge of security and privacy practices in the Internet of Things (IoT) environment.
contact tel.: 2622024341
email: info@epikentroedu.gr
Reach us at any of our branch offices.
67 Eptanisou & Karaiskaki
Heroes’ Square (Plateia Iroon)
1 Dounia St




We respect your privacy
We use cookies to offer you the best possible experience on our website. You can learn more about the cookies we use or disable them in settings. Cookie policy.
We use cookies for the operation of the site and, with your consent, for statistics. Privacy Policy
Necessary cookies are absolutely essential for the proper functioning of the website. This category includes only cookies that ensure basic functionalities and security features of the website. These cookies do not store any personal information.
Used for anonymous traffic statistics via Google Analytics. Your consent is required.